- Date
Data Ownership in Web Analytics
 Andrii Romasiun
When you add a tracking script to a website, the application starts accumulating information about who visits, what they click, and where they abandon specific funnels. That raises the practical question of who controls that accumulated information. Data ownership in web analytics represents practical control over what the software collects, why it collects it, and who can access the resulting database. It dictates where the files are stored, whether the vendor reuses the metrics, how long the records are retained, and whether you can export everything on demand.
Defining Data Ownership in Web Analytics
A practical definition: control across the data lifecycle
Ownership often sounds like a philosophical debate or a marketing slogan, but in a software context, it works best as a practical definition of control. Holding the keys to the entire data lifecycle means you dictate the collection rules and manage access permissions. You also retain the contractual right, when the agreement provides it, to pull your database out of the vendor's ecosystem, allowing you to control your dashboards, event definitions, and performance reports.
Business insights versus visitors’ personal data
You can control your business reporting without owning every piece of personal data associated with your visitors. Website operators track overall trends, conversion rates, and revenue metrics, while visitors retain individual rights over personal data connected to their identities.
Swetrix operates as a privacy-first, cookieless analytics platform that balances these two realities. The software combines clear reporting with features such as conversion funnels, custom events, revenue tracking, error monitoring, and session analysis. It also provides open API access, granular deletion controls, and a self-hosting option. This approach gives website owners practical control over business metrics without requiring them to retain more sensitive personal detail than their implementation needs. Moving away from invasive tracking does not require sacrificing the behavioral data that teams use to improve products and content.
Legal Frameworks Governing Website Analytics Data
Controller, processor, and data-subject rights
Legal frameworks approach governance through responsibilities and rights rather than a simple property model. The GDPR's controller and processor framework assigns specific roles based on who makes the decisions. The website operator generally determines why and how tracking tools are used, making that operator the controller for that specific processing activity. The analytics vendor then acts as a processor when it handles the information under the operator's instructions.
The European Data Protection Board confirms that the controller remains responsible for choosing an appropriate processor and overseeing the relationship. Its controller-processor contract guidance says the contract must cover security of processing, written authorization from the controller before engaging a subprocessor, assistance with data-subject requests, audits, and, at the controller's choice, the return or deletion of personal data after services end.
Visitors hold distinct rights under GDPR Articles 15 through 21. These include rights to access, rectify, erase, restrict, and object to processing, alongside a conditional right to data portability.
Distinguishing portability, sovereignty, and privacy
The GDPR data portability right allows individuals to receive or transfer personal data concerning them that they have provided to a controller, where processing is automated and based on consent or a contract. Because that right is limited to specific conditions and categories of personal data, it does not by itself settle whether a software vendor must hand over every aggregate metric, custom benchmark, attribution model, or derived business insight to a migrating customer. Commercial export rights for those materials depend on the vendor agreement.
Under the California Consumer Privacy Act, California's official privacy guidance describes rights to know, delete, correct, opt out, limit sensitive information, and receive equal treatment. Together, these are explicit privacy rights concerning personal information.
Furthermore, server location is one factor in determining which legal jurisdiction and transfer rules may apply. Data privacy dictates whether the processing remains lawful and fair. You can store files in a highly regulated jurisdiction and still violate privacy standards through poor event design.
Evaluating Your Analytics Platform's Data Controls
Collection, contractual use, and access
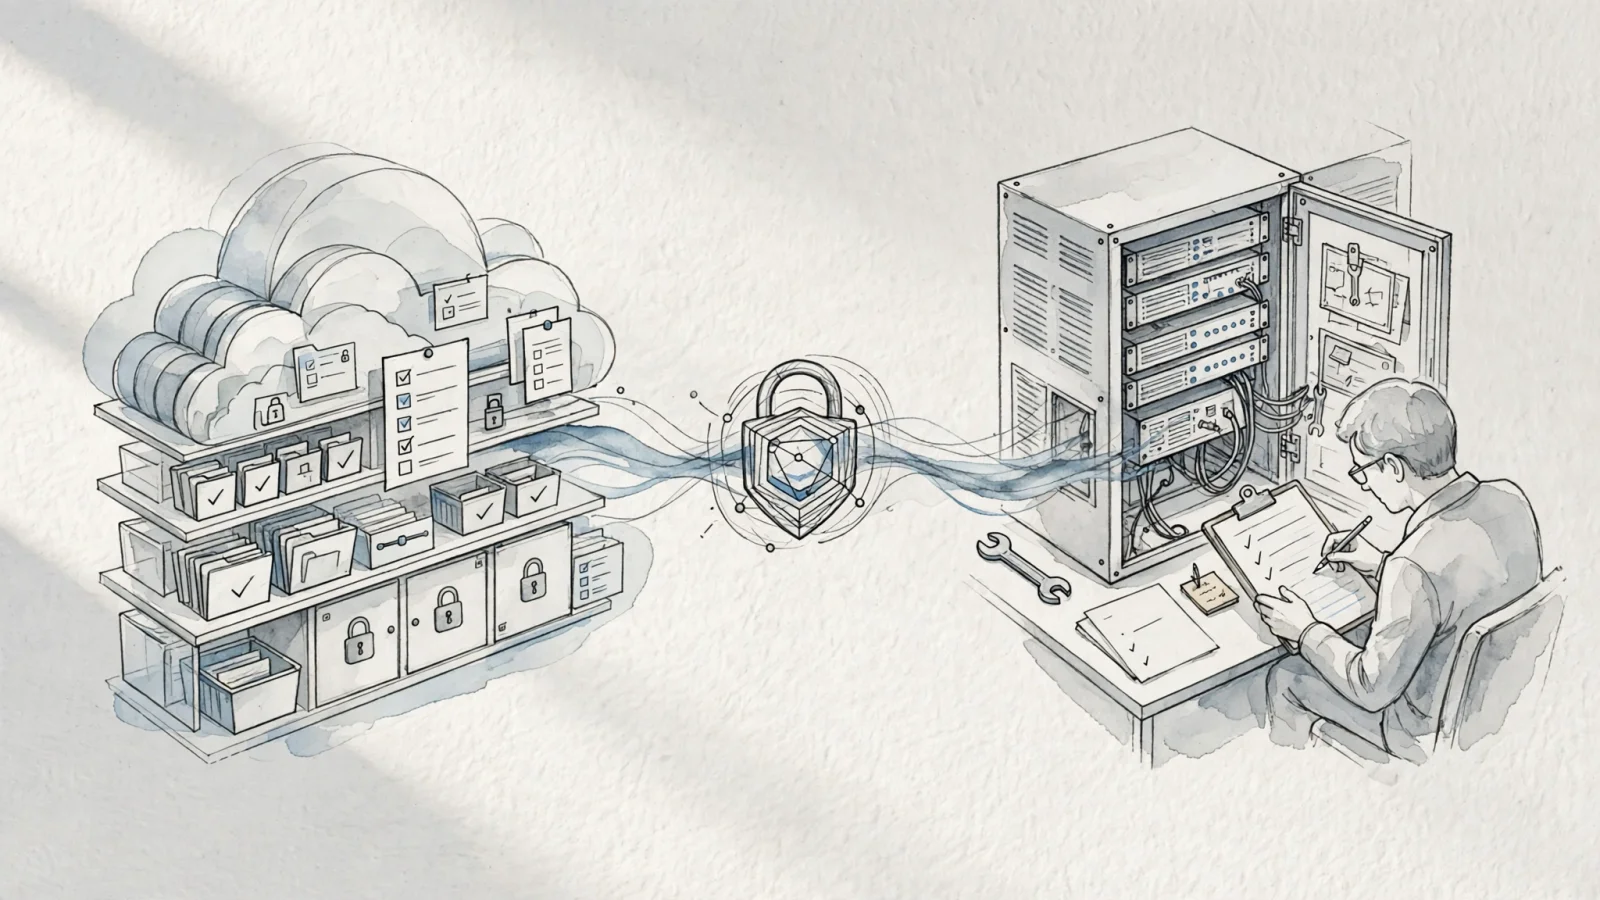
The contract sets the baseline of control, so check whether the provider claims a broad license to use your metrics for external advertising, cross-industry benchmarking, artificial intelligence training, or internal product development. If you want sole rights to the business insights, the agreement should state that arrangement clearly.
Collection controls determine what enters the database. Review the script's approach to device identifiers, IP handling, user IDs, and custom event payloads, ensuring that the platform allows you to block sensitive information before it leaves the browser.
Access permissions safeguard the collected information. Look for granular user roles, least-privilege administrative access, and support for single sign-on or two-factor authentication. The platform must also support easy offboarding workflows and formal project ownership transfers when employees or agency partners depart.
Hosting, retention, and deletion
Physical server location matters, but it is only one part of the storage architecture. Separate the primary hosting facility from support systems, third-party integrations, subprocessors, and international transfer routes. A vendor might store the main database in Europe while relying on global support ticketing systems that process IP addresses elsewhere.
Retention policies dictate the lifespan of the records. Ask whether the deletion process covers individual projects, entire accounts, session replays, and remote backups. Verify exactly how long it takes for the provider and its subprocessors to complete deletion or irreversible disposal.
Export, portability, and exit
A platform that locks your history behind a proprietary interface restricts your data ownership. Verify the availability of an application programming interface. Documented APIs should support the retrieval of raw event logs alongside aggregated reporting. Test the historical coverage, review the export data formats, and check the applicable rate limits.
| Evaluation Area | What to Verify Before Signing |
|---|---|
| Contractual rights | Does the provider claim any license to train models or benchmark metrics? |
| Collection controls | Can you disable cookies, fingerprinting, and session recordings? |
| Storage mapping | Where is the primary database, and who are the subprocessors? |
| Access and roles | Does the system support granular roles and project ownership transfer? |
| Export capabilities | Can you retrieve historical metrics and custom events via an API? |
| Permanent deletion | Does the purge process cover backups and third-party support systems? |
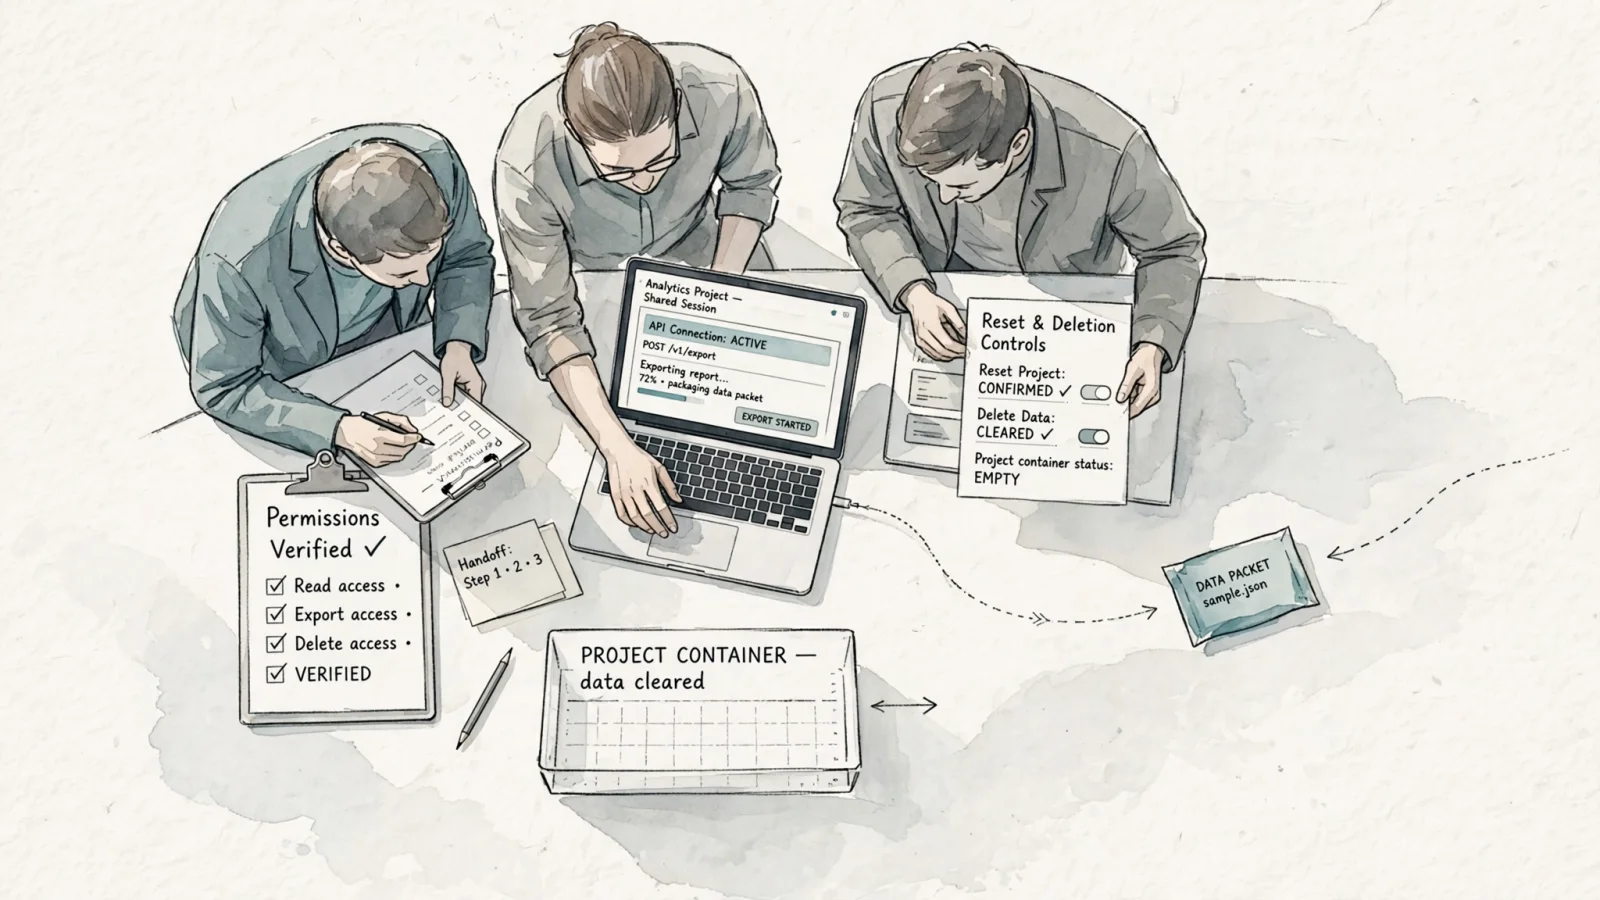
Swetrix offers concrete examples of these controls. The platform's Security Practices document states that customers retain ownership and control of their website metrics. Swetrix obtains no rights to the stored analytics. The security documentation identifies Germany as the primary analytics-data hosting location, while the same documentation lists service providers and subprocessors operating in other countries. This setup distinguishes the main hosting facility from the various processing and transfer pathways. Swetrix says customers can export analytics data through its APIs, and the API documentation describes programmatic access to aggregated analytics, sessions, profiles, custom events, and performance data. Before handoff, review the project settings and documentation for ownership transfers, project resets, and permanent deletion.
Operational details matter more than marketing slogans. Read the security documentation's subprocessor information, ask how backups are handled, and request the exact retention schedule. Request the data processing agreement, examine the data map, read the API documentation, and test a sample export workflow before deploying any script.
Choosing Between SaaS and Self-Hosted Deployment
Vendor-hosted SaaS: less maintenance, more provider reliance
Managed cloud solutions can provide immediate setup, automated updates, global content delivery networks, and uptime commitments. Providers typically handle database maintenance and security patching. This convenience requires placing trust in the vendor's contract, its chosen subprocessors, its hosting environment, and its export tools.
Self-hosted analytics: more infrastructure control, more responsibility
Deploying the application on your own servers can provide the greatest direct control over the infrastructure. You can choose the cloud account, set the physical server location, and govern internal network access. This route transfers the operational burden directly to your engineering team. You become responsible for applying security patches, managing daily backups, monitoring uptime, handling incident response, and executing retention policies. Self-hosting does not automatically make an implementation compliant, nor does it eliminate the need for a privacy notice.
| Hosting Model | Primary Advantages | Operational Trade-offs |
|---|---|---|
| Vendor-hosted SaaS | Fast deployment, managed maintenance, provider-managed backups | Reliance on vendor contracts, subprocessors, and export tools |
| Self-hosted analytics | Direct infrastructure control, custom server location | Internal responsibility for security, patching, uptime, and deletion |
| Hybrid privacy cloud | Reduced maintenance with strong contractual export rights | Requires careful review of the provider's specific terms and integrations |
Hybrid cloud: a practical middle path
A managed privacy-first cloud offers a middle path for teams needing provider-managed operations without surrendering contractual control. Swetrix supports both Cloud and Docker-based self-hosting deployments. Cloud customers avoid operating the physical infrastructure while retaining practical export and deletion rights. Organizations with strict internal governance or specific data-location requirements can run the self-hosted platform themselves. Teams without dedicated infrastructure staff may prefer the Cloud edition to avoid server maintenance, while teams with dedicated DevOps resources may choose the Docker route to keep deployment within their own infrastructure.
The Impact of Cookieless Tracking on Governance
What cookieless tracking can reduce
Moving away from browser cookies can reduce reliance on local device storage and may reduce consent prompts, but the result depends on the other technologies and data involved.
It does not answer every data governance question. The United Kingdom Information Commissioner's Office explains in its storage and access guidance that the Privacy and Electronic Communications Regulations cover more than traditional cookies, including tracking pixels, link decoration, web storage, device fingerprinting, scripts, and tags. PECR applies when these technologies store information on, or access information stored on, a user's device, although it permits certain uses in particular circumstances or with valid consent. If the information stored or accessed is personal data, UK GDPR requirements also apply.
What still needs review
Cookieless tracking can reduce consent fatigue, but the technology is not automatically compliant with GDPR, CCPA, or PECR out of the box. You must still evaluate the payloads.
Swetrix's security documentation describes its standard tracking as cookieless and says it does not collect or store personal data that can be used to identify individuals, although custom identifiers and event payloads still depend on how the site is configured. Swetrix's session replay documentation says replays start only after the site calls startSessionReplay(). Enabling replays requires a separate internal review of your legal basis, consent mechanisms, sensitive-content masking, and privacy-notice disclosures.
Run an implementation check before launching any campaign. Inspect every custom event payload and unique identifier, documenting the exact business purpose for collection. Confirm the relevant jurisdictional rules for your audience. Never pass names, email addresses, or account identifiers into custom event properties unless your documented privacy review permits it, regardless of whether the underlying script uses cookies.
Retaining Usability Alongside Privacy Controls
Cloud control without an infrastructure burden
Finding an ethical tracking alternative often forces teams to choose between invasive surveillance platforms and overly simplistic page-view counters. Swetrix closes that gap. Cloud customers receive stated ownership commitments, API-based exports, account deletion mechanisms, and access controls. You can make specific dashboards public and assign project permissions, while ownership transfers to clients should be documented before handoff. These represent operational controls over your metrics, while the ownership commitment should still be checked against the governing agreement.
Self-hosting for stricter technical requirements
Organizations operating under tight regulatory constraints often mandate direct infrastructure control. Swetrix provides a Docker-based self-hosting path that lets engineering teams deploy the stack on infrastructure they control. That setup can keep visitor data within a chosen environment, but the result depends on the network, hosting, and integration configuration. The customer assumes responsibility for database security, application patching, uptime monitoring, and permanent record deletion.
From content metrics to embedded product analytics
Retaining control of your database should not mean sacrificing the tools required for growth. The platform supports deep behavioral analysis through goal conversions, funnel visualization, and custom event tracking. Marketers monitor revenue attribution, while technical teams use real-time error tracking and performance monitoring. A robust alternative to Google Analytics needs to offer technical insights alongside traffic graphs.
These capabilities scale for business-to-business applications. Software agencies and platforms often embed Swetrix dashboards directly into their own customer portals. API access combined with embedded reporting can support that model, provided tenant-level ownership remains clear. Each individual customer must know exactly which project contains its metrics, who has access, how long the files are kept, and how to trigger a permanent deletion.
The platform extends beyond user behavior. Technical search engine optimization tools integrated into the suite allow teams to identify structural website issues. You can run an AI search LLM crawlability checker to verify how large language models read your content. When launching a new architecture, deploy the SEO migration redirect validator to validate redirect mappings during the transition. Combining these technical diagnostics with privacy-focused behavioral data creates a comprehensive view of website performance. Review the current security practices, data policies, and processing agreements to align these features with your compliance requirements.
Data Governance Evaluation Checklist and FAQs
Vendor questions to copy into an evaluation
Use this checklist to structure your next software procurement process. Ask for written answers from the vendor before deploying their script.
- Who controls the resulting database under the terms of the contract?
- What exact device identifiers, properties, and payloads does the script collect?
- Which internal systems, third-party integrations, and subprocessors can access the records?
- Where is the primary database hosted, and where does support processing occur?
- Are roles and permissions granular enough to separate internal staff, external agencies, and individual tenants?
- Can the organization export useful historical event logs and aggregated reports through an API?
- What does the deletion procedure cover, and does it include remote backups and session replays?
- What happens to the remaining files upon contract termination?
- Can the system be self-hosted, or is there a documented migration path out of the ecosystem?
Common questions about ownership, compliance, and migration
Who owns website analytics data? Under the GDPR controller-and-processor framework, the controller-processor relationship must be governed by a contract. Within that framework, the controller determines the purposes and means of processing, while the processor acts on the controller's instructions, and individuals have rights concerning their personal data.
Is data ownership the same as data privacy? The two concepts remain distinct. Data privacy requires lawful, fair, transparent, and secure processing of personal information. Data ownership defines who controls the database and what rights they possess to access, export, reuse, or delete the records. A company can exercise firm contractual control over its database while violating privacy laws through poorly designed tracking events.
Does self-hosting give you complete data ownership? Running the application on your own servers can provide greater technical control over the infrastructure and access routing. It does not automatically guarantee compliance with regional privacy laws, nor does it excuse the need for accurate privacy notices.
Does cookieless analytics mean no consent is required? Under PECR, whether consent is required depends on the technology and how it is used. The ICO explains that PECR can also apply to tracking pixels, scripts, link decoration, and device fingerprinting when they store information on, or access information stored on, a user's device. Where the information is personal data, UK GDPR requirements also apply, so removing cookies does not remove every privacy obligation.
Can businesses migrate historical metrics from Google Analytics? Migration viability depends on the target platform and the specific reporting dimensions. Before committing, confirm whether the target supports importing your GA4 exports and which dimensions it can map. Do not expect a flawless one-to-one migration of every proprietary attribution model or custom report, as the underlying schemas differ.
Does open-source software guarantee data ownership? Open-source licensing makes code easier to inspect and enables self-hosting options. It does not automatically dictate who controls a hosted database or restrict how a managed cloud provider might use the resulting metrics. Governance depends on the service terms, hosting arrangements, and export tools.
Regaining control over your web metrics requires more than swapping out a script. It requires a platform designed around transparency, portability, and granular access. Compare the managed convenience of Swetrix Cloud with the greater infrastructure control of the self-hosted Docker edition. Review the security practices and test the export controls to ensure your team retains full command over its business insights. Start building a privacy-first analytics stack at Swetrix.com.