- Date
Privacy Is More Important Than Security—But You Need Both
 Andrii Romasiun
Privacy and security perform different jobs, and neither can replace the other. Privacy sets the boundaries on what a business collects and why that data is processed. Security protects the systems and the information that remain. In website analytics, asking whether a metric is necessary comes before asking how to lock it down.
A perfectly secure system can still collect highly intrusive information that a marketing team never needed. Conversely, an ethically designed reporting dashboard with zero personal identifiers still requires strong access controls to prevent unauthorized tampering. Managing website performance requires evaluating both disciplines independently. Collecting less information limits visitor exposure, while rigorous access controls protect the aggregate trends that guide business growth.
Is Privacy More Important Than Security?
Some developers argue that privacy is more important than security, while compliance teams often reverse the priority, creating a false choice. In technical architecture, the two disciplines are distinct and complementary. Cybersecurity protects information and systems from unauthorized access, disruption, or destruction, whereas privacy addresses the risks to individuals across the entire data processing lifecycle, from initial collection through final disposal.
You need both because they address distinct failure points. Strong access controls keep outside attackers away from a database, but those same controls do nothing to stop a company from gathering unnecessary behavioral profiles on its own users.
Evaluating an analytics platform means splitting these concerns. Setting up a cookieless tool like Swetrix avoids storing persistent tracking files on a visitor's device, which reduces privacy risk by limiting long-term identification. Cookieless measurement still involves processing network signals because the software receives HTTP requests, evaluates user-agent strings, and logs page paths. With information flowing into a server, your organization decides exactly which signals serve a reporting purpose and then secures the resulting datasets against unauthorized access.
Strong Security Cannot Make Every Data Practice Private
To see where the two disciplines diverge, consider a session recording tool deployed on a checkout page. The application captures every mouse movement, scroll event, and keystroke from the visitor, and then routes this payload over TLS to an encrypted database. Only three senior engineers hold the decryption keys, and they authenticate via hardware security tokens.
Although the security architecture in this scenario is nearly flawless, the privacy outcome remains flawed. The system captures credit card numbers, passwords, and billing addresses because the input fields lack proper masking configurations. Without a data breach or unauthorized log views, the privacy violation happens entirely by design. The system collects sensitive information irrelevant to the goal of improving the website layout.
Aggregate reporting provides the opposite scenario. A basic script counts how many times a browser loads a pricing page, sending a payload that contains a URL, a timestamp, and a generic referral source. It strips IP addresses and sets no client-side identifiers. As a result, the privacy risk to the individual visitor approaches zero since the business cannot tie the pageview to a specific person.
Yet that aggregate data remains valuable to the business. If a competitor gains access to the marketing dashboard, they can map out the company's traffic patterns, top acquisition channels, and conversion rates. A deleted reporting history would also cost the marketing team its ability to measure campaign performance. The lack of personal data eliminates most privacy concerns, but the aggregate intelligence still requires strict password policies, multi-factor authentication, and regular backups.
Data Minimization Serves Both Security and Privacy
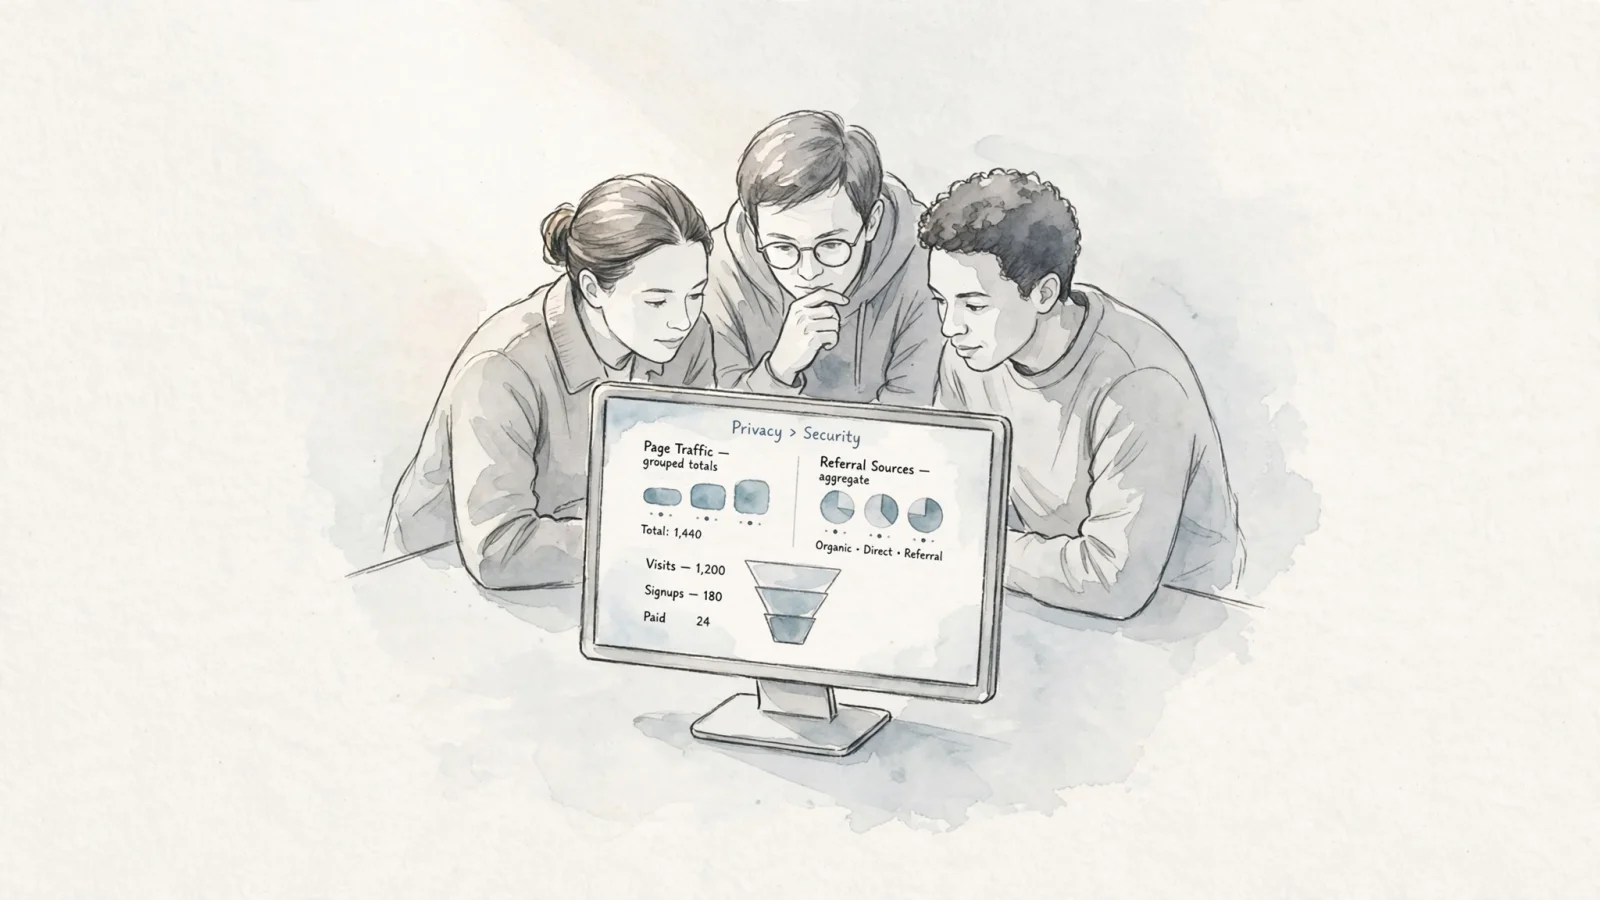
Data minimization bridges the gap between protecting users and securing systems. The principle involves identifying the exact question a report answers and then processing only the minimum viable data needed for that purpose. Data that isn't collected can't be exposed in a breach, sold by a vendor, or targeted by attackers.
This concept operates as an independent regulatory requirement. The text of the GDPR lists data minimization separately from the principles of integrity and confidentiality. Furthermore, the regulation's framework for data protection by design mandates default technical limits on the amount of personal data processed, the extent of the processing, the storage period, and accessibility.
Applying these limits to marketing analytics simplifies compliance and lowers infrastructure risk. A campaign report requires knowing how many visitors arrived from a specific newsletter link and whether they completed a signup event, rather than building a persistent profile of every article the visitor read over the past year. Configuring a tracker to drop identifying parameters before transmission solves the privacy challenge at the source.
The Federal Trade Commission reinforces this lifecycle approach to information management. In its guidance on protecting personal information, the agency recommends taking stock of all incoming data flows, keeping only what the business needs, securing the retained records, and disposing of outdated information. A lean analytics database limits liability. If a system logs raw query parameters, a developer might accidentally transmit a password reset token in a URL. Stripping those parameters before logging removes both the privacy intrusion and the security vulnerability of storing valid credentials in cleartext.
Privacy-First Analytics Measures Growth Through Aggregate Signals
Dropping persistent visitor tracking does not mean abandoning performance measurement, as teams can extract product insights from aggregate signals. The transition involves translating person-level questions into event-level metrics. When the business asks what users do, the analytics platform reports what actions occurred, separated from the identity of the actor.
Three common reporting scenarios illustrate how aggregate measurement preserves business intelligence:
| Reader | Business Question | Useful Aggregate Signals | Data to Avoid |
|---|---|---|---|
| Content creators and bloggers | Which content categories and referral sources drive newsletter signups? | Total pageviews, campaign source, category tags, and an aggregate newsletter_signup event. | Attaching email addresses, account IDs, or raw IP addresses to the signup event payload. |
| Agencies and SMB marketers | Where do visitors abandon the multi-step checkout funnel? | Landing page paths, sequential event counts, and total conversion completions. | Storing cross-site tracking IDs or person-level demographic profiles to evaluate a specific campaign. |
| B2B software companies | Can each tenant view their own usage data without exposing the broader platform? | Customer-specific reporting views, strict role-based access controls, and standardized event names. | Providing shared database access that risks exposing another tenant's raw behavioral logs. |
Swetrix bridges this gap by combining privacy-compliant tracking with product analytics. The platform reports on traffic, referral sources, and marketing campaigns without using cookies. Beyond basic pageviews, you can construct conversion funnels from defined page paths and custom events. If an agency wants to know how many visitors moved from /pricing to an add_to_cart event, the funnel report calculates the drop-off rate at each step.
This approach extends to technical optimization. Integrating a Google Analytics alternative with external datasets lets you track search visibility alongside user behavior. The Swetrix dashboard connects directly with Google Search Console, bringing query data into the same environment as landing page performance. To analyze this data further, teams use utilities like a GSC export analyzer to spot ranking drops or index coverage issues.
Product teams also run experiments without identifying individual testers. Measuring the impact of a layout change involves routing visitors to different variants and counting the subsequent conversion events. Running an A/B test calculation on those totals reveals the winning design based entirely on aggregate performance. The business learns which layout works better without learning the permanent profiles of the people who interacted with it.
Relying on aggregate metrics introduces specific limitations. A cookieless platform will not stitch together a timeline showing that a visitor clicked an ad on their phone on Tuesday and completed a purchase on their laptop on Thursday, because that level of cross-device attribution requires the identifiers a privacy-first setup intentionally discards. Acknowledging this trade-off is part of responsible data architecture.
The Limits of Cookieless Analytics
The term "cookieless" describes a storage mechanism rather than a legal exemption. Removing cookies from a tracking script stops the browser from saving a persistent text file on the hard drive. It does not automatically render the data processing anonymous, nor does it guarantee compliance with every global privacy framework.
Swetrix achieves cookieless measurement through specific, temporary processing techniques. When a browser requests a page, the analytics server receives the incoming IP address and user-agent string, processing these values in memory to generate a rotating session identifier. The platform uses this temporary hash to group a series of pageviews into a single visit. The system refrains from storing the raw IP addresses on disk, so once the processing window closes, the original network signals disappear.
This default approach handles standard pageview and event tracking safely, though higher-sensitivity features require stricter evaluation. Session replay allows product teams to watch a recreation of how a visitor navigated the layout, but Swetrix avoids recording these sessions by default. Because a replay captures the state of the document object model, it may include interactions with input fields, dropdown menus, or unmasked text, preventing the data from being automatically anonymous. Teams that use this feature configure strict masking rules for form inputs, limit the recording retention period, and restrict dashboard access to authorized personnel.
Consent Banners and Jurisdictional Rules
The primary advantage of cookieless tracking is reducing friction for the end user. In supported configurations, standard privacy-first analytics operate without triggering an intrusive cookie-consent banner. If the script avoids accessing information stored on the device and avoids building a profile for targeted advertising, many regulatory frameworks permit processing based on legitimate business interests.
However, a single analytics script does not clear a website of its compliance obligations. If you install a separate retargeting pixel or use local storage to track user preferences across sessions, the site still requires a consent mechanism.
Regional regulations also dictate specific exemptions. As of November 13, 2026, UK website operators manage updates to the Privacy and Electronic Communications Regulations. Section 112 of the Data (Use and Access) Act 2025 took effect on February 5, 2026, introducing a narrow statistical-purposes exception for device storage and access.
The ICO's guidance on cookies and similar technologies says PECR requires organizations to tell people if they set cookies, explain what the cookies do and why, and obtain consent. It lists two exemptions: cookies used solely to transmit a communication over an electronic communications network, and cookies strictly necessary to provide an online service requested by the subscriber or user; helpful or convenient cookies still require consent.
Implementing Privacy-First Analytics
Building a resilient measurement strategy requires treating data as a liability rather than an unlimited asset. A platform like Swetrix provides tools to monitor traffic and conversions safely, but the implementation dictates the final risk level. Following a structured checklist helps developers and marketers align reporting goals with security obligations.
- Define the business decision before choosing a feature. Write down the exact question the dashboard answers. If the goal is optimizing a checkout flow, ordered funnel steps prove necessary, while cross-site tracking IDs do not.
- Select the smallest viable set of signals. Collect the total number of pageviews, referral sources, and distinct event names. Reject configurations that append granular user data to basic traffic reports.
- Keep identifiers out of the analytics payload. Audit your tracking scripts to ensure names, email addresses, customer account IDs, and session tokens never pass into event properties, page titles, or URLs.
- Control higher-sensitivity features. Treat tools like session replay as specialized diagnostics rather than default tracking. Enable masking for all text inputs, exclude pages that handle billing information, and set aggressive deletion schedules for the recordings.
- Secure the retained information. Inventory where your aggregate data flows. Restrict dashboard access to staff members who actively run reports. Implement multi-factor authentication, and document a clear incident response plan for unauthorized access attempts.
- Map the site's total compliance footprint. Evaluate your analytics provider alongside your hosting infrastructure, CRM integrations, and advertising pixels. Ensure your privacy policy accurately reflects the data your organization processes, and configure consent notices based on the combined behavior of all active scripts.
Transitioning to privacy-first measurement means rethinking how you value data. Focusing on aggregate trends and custom events allows teams to optimize websites without collecting unnecessary liabilities. Swetrix offers a complete cookieless alternative to legacy analytics platforms, combining GDPR-compliant traffic reporting with product insights like funnels and A/B testing. To see how much actionable intelligence your team can gather without tracking individual visitors, explore the dashboard at swetrix.com.