- Date
IP Address Lookup: What It Can and Can't Reveal
 Andrii Romasiun
When a server receives a request for a webpage, it uses the origin Internet Protocol (IP) address to route the data back to the correct destination. Because these numbers identify connections, many assume a direct map exists between a network identifier and a physical location. An IP address lookup can return an estimated region or network operator, but it cannot verify a residential street address. A public lookup provides routing and registration data rather than personal identity.
Website owners routinely use geographical data to understand aggregate traffic patterns. This context helps you localize content and optimize server loads based on regional demand. Collecting this information does not require archiving raw network addresses. Our standard analytics platform at Swetrix processes visitor IP addresses transiently to determine the session duration and broad geolocation, discarding the raw data rather than storing it. Our data policy outlines how this approach delivers country, region, and city reports without treating a network node as a persistent visitor identity.
Public and Private IP Addresses Are Different
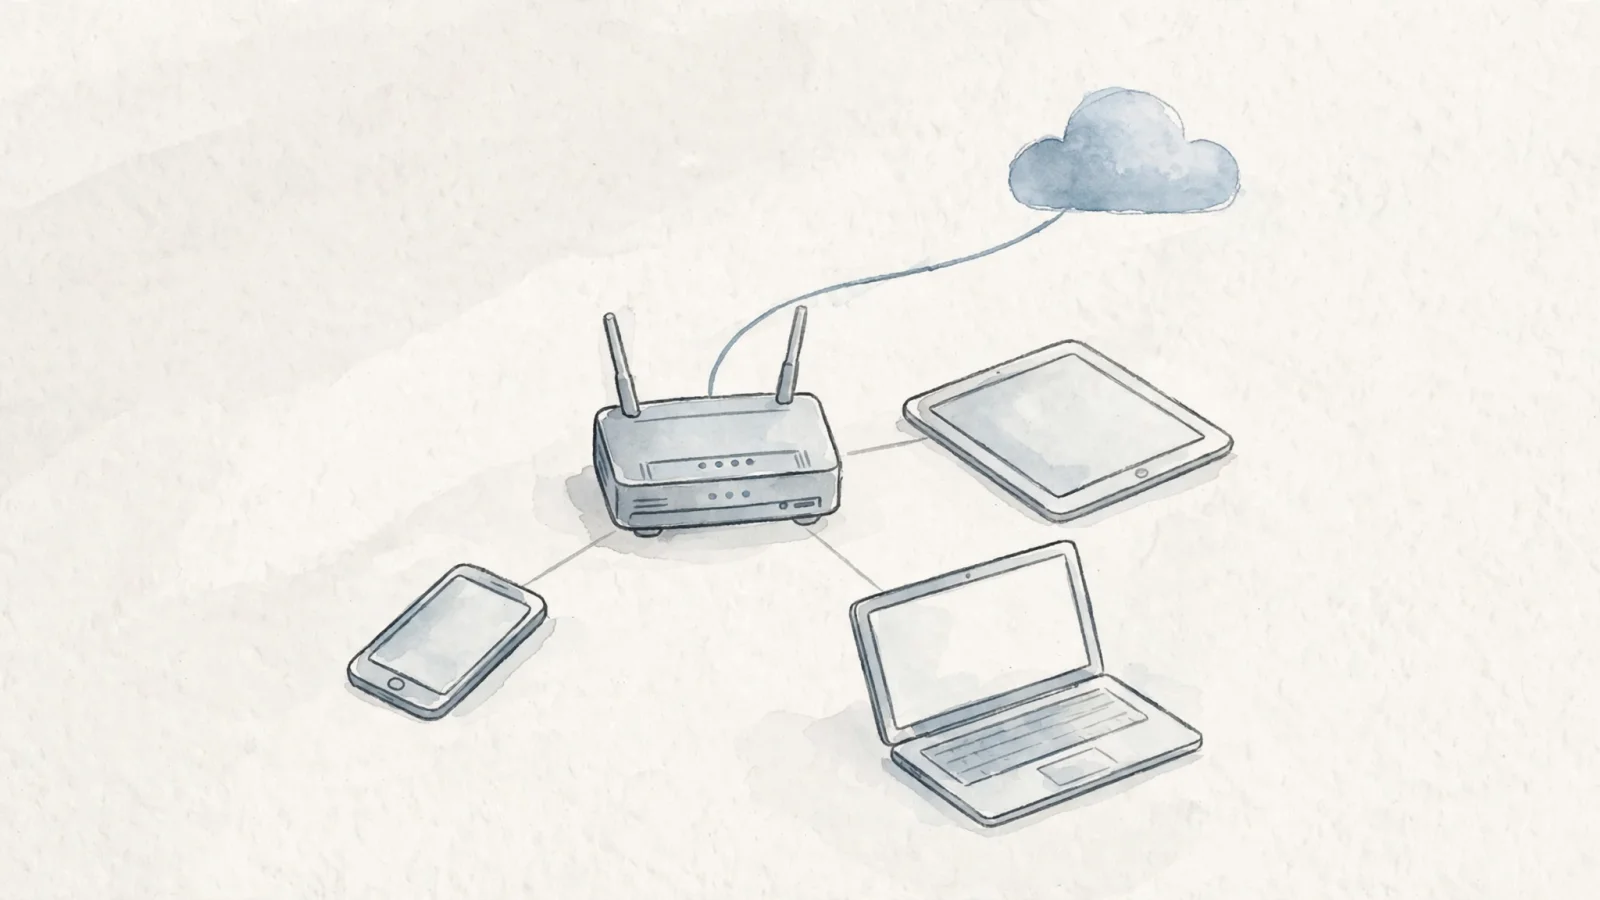
Network addresses operate on two different levels to conserve available numbers and secure local devices. A public IP is the address an outside service sees when your home or office network communicates with the wider internet. Your internet service provider assigns this number to your modem or gateway router, although some providers share public addresses through Carrier-Grade NAT. Web servers, streaming services, and analytics platforms receive this public address with requests, which gives the network a return address for response traffic.
Meanwhile, your router manages a separate internal network. It assigns a private IP address to every laptop, phone, and smart appliance inside that space. These private addresses hold no global meaning, which means they cannot be routed across the public internet. They exist solely so your router knows which internal device requested a specific packet of data. Opening a website on your phone prompts the router to translate your private address into the shared public address before sending the request outward.
Private networks use specific address blocks reserved for private internets. IETF RFC 1918 lists the three address blocks that the Internet Assigned Numbers Authority reserved for that purpose: 10.0.0.0/8, 172.16.0.0/12, and 192.168.0.0/16. So an address beginning with 192.168 falls within the private address space.
Reviewing these numbers reveals two different formats. The Internet Assigned Numbers Authority coordinates IP addressing globally, and IPv4 addresses are 32-bit numbers often expressed in dotted-decimal format, such as 192.0.2.53. IPv6, deployed later, uses 128-bit numbers conventionally expressed as hexadecimal strings, as in 2001:0db8:582:ae33::29. Both are types of IP addresses in active use.
Three IP Lookup Types, Three Different Results
Running a query on a network address yields different data depending on the lookup method. People often conflate these tools, expecting a single search to reveal a physical location, a corporate owner, and a server name. Instead, each protocol queries a different database to return a distinct piece of network metadata.
IP Geolocation: An Estimated Area
Geolocation relies on commercial databases that map IP blocks to geographic regions. Vendors build these datasets by analyzing data feeds from service providers, measuring latency across network nodes, and tracking regional searches tied to specific connections.
The resulting location is an estimate. As Cloudflare's geolocation documentation explains, nothing inherently binds an IP address to a physical location or country. Because IP addresses rotate and ownership can change, geolocation data is dynamic and may shift over time.
RDAP or WHOIS: Network Registration
The Registration Data Access Protocol (RDAP) and the older WHOIS system query the regional internet registries that manage global address distribution. These registries record which corporate entity controls a specific block of numbers.
Running an RDAP query on a public address returns the network operator, the autonomous system number, and administrative contact details. Registration data identifies the corporate internet service provider or hosting company holding the allocation, rather than the individual customer leasing the connection. As the American Registry for Internet Numbers points out in its public safety documentation, these records do not guarantee the physical location of the active network equipment.
Reverse DNS: A Configured Hostname
A reverse DNS lookup queries the domain name system to find the hostname associated with an IP address. While a standard DNS query translates a domain name into an IP address, a reverse lookup relies on a Pointer (PTR) record to perform the opposite action.
Network administrators manually configure these PTR records for their servers, often creating reverse lookup zones to help mail servers verify sending domains and filter spam. Because the server operator writes the PTR record, the resulting hostname is a configured text string. This makes reverse DNS a network management tool rather than a method for reverse geolocation or postal address discovery.
| Lookup Type | Database Queried | Data Returned | Primary Use Case |
|---|---|---|---|
| Geolocation | Third-party commercial datasets | Estimated country, region, city | Localizing content, targeted analytics |
| RDAP / WHOIS | Regional Internet Registries | Network operator, allocation block | Identifying ISPs, routing abuse reports |
| Reverse DNS | Domain Name System (PTR) | Configured hostname | Server verification, mail authentication |
Why Network Locations Differ From Street Addresses
The disconnect between a network identifier and a physical street address stems from how modern internet infrastructure scales. Service providers manage limited pools of addresses and distribute them dynamically, so the address assigned to a modem today might belong to a different customer in a neighboring city next week.
Address sharing actively degrades geolocation accuracy. Mobile network operators and residential ISPs frequently deploy Carrier-Grade NAT to stretch limited IPv4 allocations, placing a secondary translation boundary inside the provider's network. Thousands of cellular customers connected to different cell towers might share a single public IP address. This sharing reduces the confidence and granularity of any IP-based location estimate. Mapping a shared mobile gateway usually yields coordinates that reflect the provider's data center instead of the user's mobile device.
Privacy tools and routing services further separate the origin device from the visible network address. Browsing a website through a virtual private network means the site logs the public address of the VPN exit node. Privacy proxies and enterprise secure web gateways routinely shift or obscure geolocation results. If a user in London connects to a VPN server in Tokyo, the website's analytics record a visit from Japan.
Geolocation database mechanics also introduce visual artifacts that users misinterpret as precise tracking. When a vendor only knows the country or state associated with an IP block, the software assigns default center-point coordinates for that region. An analytics dashboard mapping those coordinates might drop a pin on a specific farm or a lake sitting at the exact geographic center of the state, leading website owners to mistake default regional coordinates for pinpointed physical addresses.
The fluid nature of network routing prevents public databases from tracking individual endpoints. Law enforcement agencies investigating cybercrime rely on public RDAP data to identify the specific internet service provider, rather than using lookup tools to find a physical address. Investigators can then use legal process to request the provider's internal connection and subscriber records for the relevant time, which may link a temporary address assignment to a customer account. Without access to the ISP's internal subscriber records, a public IP lookup cannot identify a home address.
How to Find Public and Private IP Addresses
Checking a network configuration requires looking in two different places. Finding the public address involves asking an outside server what number it sees, while checking the private address requires querying the local operating system.
A browser search for "what is my IP address" returns the public IPv4 or IPv6 address. The search engine reads the source address attached to the HTTP request and prints it on the screen, making this the fastest way to confirm the address a network presents to the outside world. Activating a VPN or a corporate proxy before running the search displays the proxy server's address instead of the residential connection. Reviewing the network request with an HTTP headers checker helps developers see if intermediate proxies are appending secondary routing information to their traffic.
Finding the private address requires checking the device settings, because the operating system maintains the local connection details assigned by the router. Windows users view their local IPv4 address by opening the Network & Internet settings panel and selecting their active Wi-Fi or Ethernet connection properties. Mac users find the same local address under the Network panel in System Settings. Mobile users tap the information icon next to their active Wi-Fi network to view the private assignment.
Responsible Use of IP-Derived Data in Analytics
Understanding the limitations of network tracking directly impacts how you handle visitor data. Because an IP lookup alone does not reveal visitor behavior or prove personal identity, relying on raw network addresses for user tracking creates privacy risks. Modern privacy regulations like the GDPR and CCPA can treat IP addresses as personal data, depending on context, prompting organizations to manage consent and data retention carefully.
A privacy-first Google Analytics alternative such as Swetrix can reduce privacy risks while maintaining rich geographic insight. Swetrix standard analytics provides country, region, and city context by processing the incoming IP address transiently. The platform uses the address to determine the initial geolocation and secure the current session, then immediately discards the raw data. This architecture avoids client-side identifiers, which means this analytics setup may not require a cookie consent banner, depending on your broader site and applicable rules.
Broad product analytics provide much deeper insight than a basic network lookup offers. Website growth depends on understanding how visitors navigate a site, where they encounter friction, and which marketing campaigns drive conversions. Swetrix delivers custom event tracking, conversion funnels, A/B testing, and error monitoring without relying on persistent network identification.
Implementing these tools on complex web architectures requires careful network configuration. Deploying server-side integrations or embedding analytics into a B2B platform means the application server makes the request to the analytics endpoint rather than the user's browser. The Swetrix Events API relies on developers forwarding the original visitor's network data using the X-Forwarded-For header when appropriate. If the server fails to forward this header, the analytics dashboard logs the data center's location and registers all traffic as originating from a single source.
Network data also helps clean aggregate reporting, since internal company traffic heavily skews conversion rates and engagement metrics. The Swetrix project configuration settings allow administrators to block specific network addresses or entire CIDR ranges. Adding the corporate office's static allocation block to this exclusion list ensures the analytics dashboard only reflects external visitors.
While transient processing protects raw network data, configuring behavioral tracking tools requires attention to detail. Advanced features like session replays capture the user interface as the visitor experiences it. These replays occasionally contain personal data, depending on what a page displays and how the project administrator configures the privacy masking settings. Reviewing form fields and sensitive page elements keeps the analytics implementation compliant with regional privacy laws.
Analyzing geographic trends helps businesses scale, but raw network addresses carry a high compliance burden. Discarding this data after extracting the region provides all the necessary context for growth while respecting visitor privacy.
Ready to track your global audience without archiving their network data? Try Swetrix for a privacy-first, cookieless analytics dashboard that delivers detailed geographic reports, conversion funnels, and performance insights out of the box.