- Date
CSP Validator: Check and Test Your Policy
 Andrii Romasiun
A Content Security Policy helps prevent unauthorized scripts from running on your website, because browsers enforce these rules to limit cross-site scripting vulnerabilities and prevent malicious data injections. Writing a policy requires exact syntax, and testing it requires confirming what the server sends. A CSP validator inspects a proposed policy string or a live response header to identify broken formatting, unintended blocks, or overly permissive rules. Testing changes before rollout helps you patch security gaps without taking down forms, media embeds, or analytics tools.
What a CSP Validator Does
Content Security Policy tells browsers what sources or behaviors a page is allowed to execute. It acts as a defense-in-depth measure against attacks that attempt to run malicious code in a user's browser, which is why the MDN CSP guide describes it as a secondary layer of mitigation against cross-site scripting vulnerabilities.
Validation takes different forms depending on the tool you use. Some tools read a text string and check its syntax, while others ping a URL to see what the server returns in its HTTP headers. The Swetrix CSP Checker inspects a live response header, generates a starter policy for your site, and flags structural problems while formatting the output for readability.
A passing syntax check does not prove the policy is secure, because a policy can be perfectly formatted and still allow malicious inline scripts if the directives are too broad. CSP reduces risk, but it does not stop every attack or replace secure coding practices like input validation and output encoding. Validation tools identify structural errors and highlight missing directives rather than certifying a web application as impenetrable.
Three Checks That Answer Different Questions
Different validator tools can perform different jobs, and knowing which check you need prevents false confidence. A syntax error can cause a directive to be ignored, while a logical error might leave your application exposed.
| Check | What it answers | Useful for |
|---|---|---|
| Syntax and policy parsing | Can the string be parsed and how are directives interpreted? | Reviewing a draft policy text before deployment |
| Live-header check | What Content-Security-Policy does a particular URL return? | Checking what visitors' browsers receive |
| Security and runtime review | Does the policy contain bypasses and does the site still function? | Reducing risk and avoiding broken pages |
Start by inspecting the live header. A syntax parser cannot tell you if your server is sending the header to users, since a proxy, load balancer, or content delivery network might strip the header before it reaches the client. You can use Swetrix to ping the exact URL and verify the network response.
Once you have a valid header, a separate security evaluation helps identify logical flaws. The Google CSP Evaluator reviews a provided policy for potential XSS weaknesses. It accepts a draft policy, includes a version selector, and helps identify subtle CSP bypasses. This operates strictly as a convenience tool, meaning a passing grade from an evaluator gives no security guarantee.
Browser testing handles the final job. An evaluator can flag policies that may allow unauthorized scripts, but browser testing reveals whether the policy also blocks your own checkout button. These three checks overlap to cover parsing, delivery, and behavior so they complement rather than replace one another.
Check the Header Your Website Serves
You might configure a policy on a primary domain and assume it applies everywhere, but servers often return different policies for different routes, representations, or deployment environments. A staging environment might run an open policy while production enforces strict rules, or a marketing page might have entirely different script requirements than an authenticated application dashboard.
Test the exact URL and environment you care about, because a generic domain check misses specific route configurations. The W3C CSP specification identifies the HTTP response header as the preferred method for delivering a policy, superseding HTML meta tags that cannot support all features.
Enter the target URL into the Swetrix CSP Checker to inspect its returned header. The tool displays the exact data the browser receives from the server. You can also run a full HTTP headers check to view every security header your server sends alongside the policy. If your site lacks a policy entirely, the Swetrix checker includes a generator to build a starting point covering scripts, styles, images, frames, and connections.
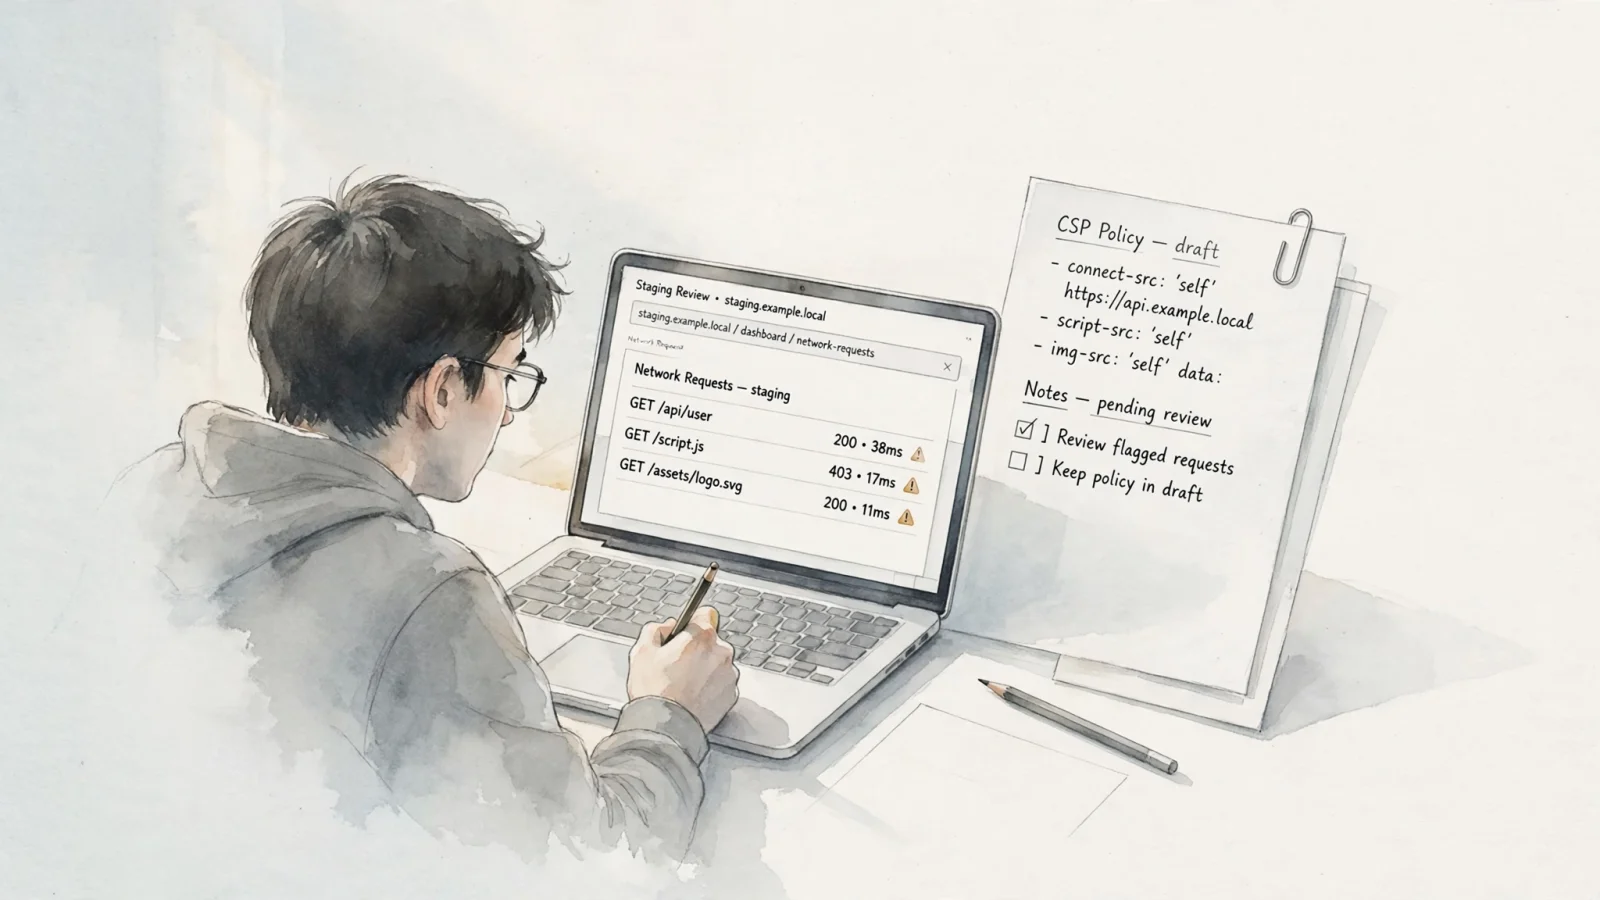
Check suggested sources against your application dependencies before applying them, since a generated policy relies on common assumptions. You might host images on an external domain or use a third-party payment iframe that the default generator omits. Inspect the network requests of your application to build a policy that fits its technical requirements.
Read the Policy Before You Change It
Policies use specific directives to control different types of resources. Understanding how these directives interact prevents accidental breakage when you lock down a previously open site.
| Directive | Plain-English role |
|---|---|
default-src | Fallback for fetch directives that are not specified separately |
script-src | Controls permitted script sources |
connect-src | Controls connections made by page scripts, such as analytics requests |
img-src, style-src, font-src | Control image, style, and font sources |
frame-src | Controls frames the page can load |
frame-ancestors | Controls which sites may embed the page |
object-src, base-uri, form-action | Additional controls for embedded objects, base URLs, and form submissions |
The default source acts strictly as a fallback. If you set a default source but define an explicit script source, the explicit directive governs all scripts, leaving the default to apply only to fetch requests that lack a specific directive in the policy string.
The OWASP Content Security Policy Cheat Sheet explains that frame-ancestors controls who may embed a page and does not fall back to the default source. This distinction matters for business-to-business software. A starter example might restrict all framing by setting frame-ancestors 'none', which suits a standard blog but fails immediately for a product designed to appear inside a customer's admin panel.
For embedded products, review both the parent page's frame source and the embedded page's frame ancestors. A restrictive policy blocks legitimate application features if applied without auditing the product's intended integrations. Read the directives, trace them back to the features they control, and adjust them to match your architecture.
Test a Stricter Policy Before Enforcing It
Deploying a new policy directly to production can break existing functionality. Browsers block resources that violate CSP, so an untested rollout can disable sign-in forms, break stylesheets, and prevent analytics scripts from firing.
Start with a proposed policy using the Content-Security-Policy-Report-Only response header. This mode monitors the policy and reports violations without blocking any resources, letting you observe what would break before it impacts your visitors.
Browsers require you to send report-only policies as HTTP response headers instead of HTML meta elements. The MDN documentation for the report-only header details how to configure reporting endpoints. To route reports, define an endpoint in the Reporting-Endpoints response header and select it with the report-to directive; the documentation shows the legacy report-uri directive alongside it because report-to does not yet have full cross-browser support.
When the report-only header runs, test real user journeys. Navigate through pages with forms, video embeds, checkout flows, and third-party marketing tools. After reviewing the browser console errors and network requests, check your reporting endpoint for aggregated violation data. You will likely see noise from browser extensions injecting scripts into the page, so filter out the extension traffic to focus on violations triggered by your own application code.
Fix violations by adding specific sources to the correct directives. Resist adding unsafe inline execution ('unsafe-inline') or unsafe evaluation ('unsafe-eval') merely to silence console errors, because those bypasses weaken the restrictions the policy exists to enforce. Use nonces or hashes to permit intended scripts safely. A nonce generated uniquely for each server response is one secure approach. Enforce the policy by switching to the standard enforcing header only after all required application behavior works smoothly in report-only mode.
Keep Analytics Working Under CSP
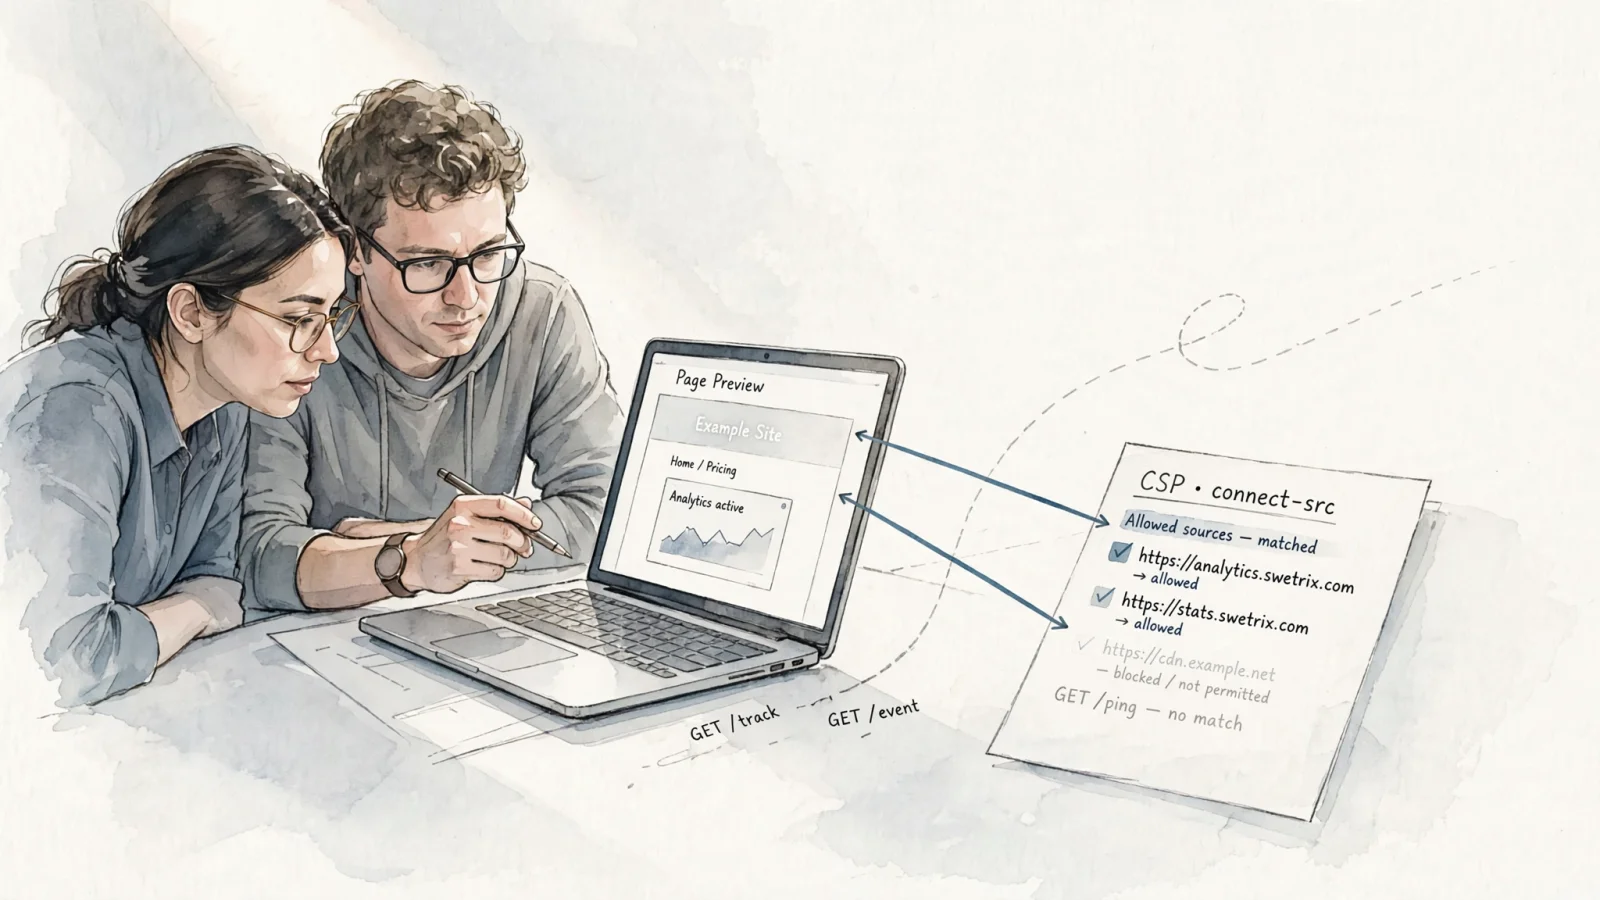
A strict policy blocks analytics platforms and the API requests they send, requiring you to permit the tracking tool in both the script directive and the connection directive.
Browsers apply these security rules uniformly, even if you transition to a privacy-first, cookieless Google Analytics alternative like Swetrix. CSP restricts network behavior regardless of cookie usage. The browser requires permission to download the script file, and the script requires permission to send data beacons back to its server. If either permission is missing, the request fails and the browser may report a CSP violation in the console.
The current Swetrix starter example lists https://cdn.swetrix.com under the script source and https://api.swetrix.com under the connection source. Double-check these URLs for your specific setup. If you self-host the platform or use a custom domain, allowlist your own configured endpoints instead of the public Swetrix CDN.
Inspect the script and requests in your browser's developer tools after a policy change. Open the network tab, refresh the page, and navigate through a few links. Swetrix troubleshooting documentation states that network requests to its hosted API should return an HTTP status 201. A status of 0, a blocked request warning, or a missing network call indicates the connection directive lacks the correct endpoint.
Content Security Policy limits browser exposure to malicious scripts and unauthorized embeds, but it provides security rather than privacy. It does not establish cookie consent, GDPR compliance, or privacy law adherence. Choose analytics tools that respect user privacy by design, and configure your policy to secure the browser environment around them.
CSP Validator FAQs
How Do I Check My Website's CSP Header?
Inspect the live URL of the specific page you want to review. You can use a header checker like Swetrix to view the policy the server returns to the browser. Different deployment environments or specific application routes often return different policies, so checking the homepage alone is insufficient.
Is a CSP Validator the Same as a Security Evaluator?
A syntax validator checks syntax, while a live-header checker confirms the server delivers the header correctly over the network. A security evaluator reviews a parsed policy for potential bypasses, open allowlists, or structural weaknesses. A valid policy string might still be too permissive to stop an attack.
Does CSP Prevent Every XSS Attack?
Content Security Policy restricts unauthorized sources and can block inline script execution when the policy disallows it, acting as a secondary defense layer rather than preventing every cross-site scripting attack. It never replaces secure coding practices like rigorous input validation and context-aware output encoding.
Transitioning to a strict policy requires careful testing, but securing your frontend should never cost you your site data. Swetrix provides a privacy-first, cookieless analytics platform alongside built-in SEO and security utilities. Inspect your live header with the Swetrix CSP Checker, evaluate your proposed changes in report-only mode, and keep measuring your product growth securely without compromising user privacy.