- Date
CCPA vs GDPR Requirements for Website Analytics
 Andrii Romasiun
Evaluating CCPA vs GDPR requirements starts by looking past the cookie banner on your homepage to understand how each framework defines its reach. These two laws dictate how you collect, process, and store visitor information, but each defines its requirements differently. The General Data Protection Regulation builds its scope around territorial reach and the processing of personal data. The California Consumer Privacy Act, amended by the California Privacy Rights Act, bases coverage on a for-profit business’s connection to California and specific revenue or data-processing thresholds.
Neither framework serves as a universal cookie rule. A site can fall under GDPR jurisdiction and may not need an analytics consent banner if its tool does not store or access information on a visitor’s device, its personal-data processing has an appropriate lawful basis, and other site scripts follow separate device-access rules. Compliance means evaluating who your visitors are, what your company earns, and how your analytics vendor handles the data it collects.
That distinction also matters when choosing an analytics setup. Moving from Google Analytics to cookieless tracking need not mean giving up essential growth data such as conversion funnels, session replays, or technical SEO insights, but teams should confirm how each platform or complementary tool provides the capabilities they need. Swetrix bridges straightforward, privacy-focused tracking and advanced product analytics, helping teams assess privacy alongside the growth data they rely on.
Comparison of Scope, Rights, and Vendor Rules
A privacy review should follow data flows rather than a tool’s marketing label. The table below outlines how these two frameworks handle the mechanisms of website tracking, data definitions, and vendor management.
| Requirement Area | GDPR Framework | CCPA/CPRA Framework |
|---|---|---|
| Primary Scope Test | An organization established in the EU, or one outside the EU that offers goods or services to people in the EU or monitors their behavior there. | A for-profit business that does business in California, determines why and how personal information is processed, and meets a revenue or data-volume threshold. |
| Information in Scope | Personal data relating to an identified or identifiable natural person, including online identifiers and IP addresses when they can identify or be linked to someone. | Information that identifies, relates to, or could reasonably be linked to a consumer or household. |
| Lawful Basis and Consent | Every processing purpose requires a lawful basis; consent is one option, while legitimate interest is another. | Generally relies on notice and opt-out rights rather than prior opt-in consent for routine analytics; covered businesses must honor applicable sale/sharing opt-outs and preference signals. |
| Consumer Rights | Access, rectification, erasure, restriction, portability, and objection, subject to legal conditions. | Right to know, delete, correct, opt out of sale or sharing, limit certain sensitive data uses, and equal treatment. |
| Analytics Vendor Roles | Requires determining if the vendor is a processor, controller, or joint controller, supported by a data processing agreement. | Requires checking if the vendor acts as a service provider or contractor, and if independent data use constitutes a sale or share. |
| General Response Time | One month for most requests, with a possible extension of up to two further months for complex cases. | 45 calendar days for requests to know, delete, or correct, with a possible 45-day extension; opt-out and sensitive-information limitation requests are due within 15 business days. |
What GDPR Requires for Website Analytics
The GDPR's territorial-scope test is based on territory rather than a revenue test. The law applies to relevant personal-data processing by an organization established in the EU, along with organizations outside the EU that offer goods or services to people there or monitor their behavior in the EU. If a blog based in Canada targets people in Germany with its services or monitors their behavior while they are there, that processing can fall under the regulation.
Personal Data and Lawful Basis
The regulation defines personal data broadly. IP addresses, custom event identifiers, and detailed browsing records can qualify when they identify or can be linked to an identifiable person. Applying a hash function to a user ID or replacing a name with a pseudonym does not render the information anonymous, because it remains in scope if you or your analytics platform can re-identify the visitor by combining datasets.
Every processing activity requires an applicable lawful basis before processing begins. The official GDPR text outlines several options, including consent and legitimate interests, so consent is not the only available basis. An organization measuring aggregate server loads without persistent user identifiers might consider legitimate interests if the processing is necessary and the impact on visitors’ rights is proportionate. That assessment may change if the platform tracks users across domains or profiles their behavior for advertising.
Rights, Notices, and Vendor Obligations
You must provide clear transparency notices explaining what data you collect, why you need it, and how long you retain it. Visitors hold specific rights to access their data, rectify inaccuracies, erase records, restrict processing, port their data to another service, and object to certain activities. When a visitor submits a valid erasure request, you generally have one month to respond, though complex cases can extend that period by up to two further months.
Meeting these obligations requires classifying your analytics provider accurately. A vendor acting as a data processor handles personal data only on documented instructions from the data controller. If the analytics company uses your visitors' data to improve its distinct products or build cross-site profiles, it may become a controller or joint controller. Processor relationships require binding terms that mandate security measures, limit data usage, and assist you in handling visitor rights requests.
What CCPA/CPRA Requires for Website Analytics
California traffic alone does not establish coverage under the California Consumer Privacy Act. The California Privacy Rights Act amended the original legislation rather than creating a separate law, refining the thresholds that bring a business under its jurisdiction.
Coverage Tests and Information in Scope
The framework generally covers a for-profit business doing business in California that collects consumers' personal information, determines why and how it is processed, and meets at least one qualifying test. The CPPA's current FAQ lists three thresholds: annual gross revenue of $26.625 million or more in the preceding calendar year; buying, selling, or sharing the personal information of 100,000 or more California residents or households; or deriving 50 percent or more of annual revenue from selling or sharing California residents’ personal information.
Information that identifies, relates to, or could reasonably be linked to a consumer or household is personal information, and the CPPA FAQ lists internet browsing history and inferences about preferences and characteristics as examples. The FAQ also says California residents who are employees, job applicants, or contacts for business customers, vendors, or independent contractors have CCPA rights. So, if it meets the CCPA coverage test, a B2B software company should account for personal information collected about California-resident visitors to its marketing site, just as an ecommerce retailer does for its shoppers.
Notices, Rights, Opt-Outs, and Vendor Contracts
California law centers on transparent notice at collection and robust consumer rights. Residents hold rights to know what information a business collects, delete those records, correct inaccuracies, opt out of the sale or sharing of their information, and limit specific uses of sensitive personal information.
Requests to know, delete, or correct generally require a response within 45 calendar days, and businesses can extend that period by another 45 days after notifying the consumer. Meanwhile, sale and sharing opt-outs, alongside sensitive-information limitation requests, must be handled as soon as feasible and within 15 business days. The same FAQ says covered businesses must honor qualifying opt-out preference signals, such as Global Privacy Control, as valid requests to stop selling or sharing personal information.
Analytics vendors fit into this structure based on their contracts and data practices. A service provider or contractor processes information only for the business purposes specified in a written contract. If an analytics platform uses your site traffic to build ad-targeting segments for other clients, that practice may qualify as a sale or sharing, depending on the data flows and contracts. If so, a covered business must honor applicable opt-outs and provide the required method for consumers to exercise the right, such as a visible "Do Not Sell or Share My Personal Information" link where required.
2026 Rules and the 2027 ADMT Start Date
California privacy regulations continue to evolve. The CPPA's final-rule announcement says the package took effect January 1, 2026, adding cybersecurity-audit and risk-assessment requirements for businesses subject to those rules, with compliance and reporting deadlines for some requirements extending to later years. The announcement identifies businesses subject to risk-assessment requirements but does not list the processing activities that trigger an assessment, so teams should consult the final regulations to determine whether their analytics activities are covered.
Businesses also face automated decisionmaking technology requirements, and the CPPA says requirements for ADMT used in significant decisions begin January 1, 2027. For those decisions, including those related to employment or financial services, the FAQ says consumers have a right to notice, to opt out where applicable, and to request meaningful information about how the ADMT functioned and affected them.
Do Website Analytics Cookies Require Consent?
The GDPR requires a lawful basis for processing personal data, but it does not set the rules for browser storage. Separate EU ePrivacy rules, implemented through national laws, govern storing information on or accessing information from a visitor's device. This distinction explains why cookie banners exist.
In France, CNIL's analytics guidance says site and app operators generally must inform users of cookie purposes, obtain consent before depositing or reading cookies or other tracers, and provide a means of refusal. For audience measurement, the guidance allows an exemption only when a tracer meets its listed conditions, while noting that the ePrivacy Directive may be subject to national variation.
Choosing a cookieless analytics platform helps address device-access rules, but cookieless tracking does not automatically guarantee total anonymity. You must evaluate what information reaches the server and what data the payload contains. A system that avoids cookies but fingerprints the browser through font rendering, screen resolution, and hardware concurrency to build a permanent profile faces regulatory scrutiny.
Audit Your Analytics and Vendor Setup
Evaluating your compliance requires documenting exactly how data moves from a visitor's screen to a vendor's database. Consent requirements depend on how each analytics script accesses a visitor’s device and shares data, so auditing your setup helps identify whether your current tools require a banner.
Map Tags, Device Access, and Event Data
Start by inventorying every analytics script, advertising pixel, and embedded media widget on your domain. Use your browser's developer tools to inspect changes to browser storage and review the network requests each script sends to external servers. Then examine the payloads for IP information, requested URLs, query strings, and custom event properties, and review retention policies.
URLs and custom event fields can inadvertently capture names, email addresses, or sensitive account details. When a visitor submits a form and the resulting URL reads ?user=john.doe@email.com, your analytics platform will index that personal data unless you configure the tool to strip query parameters.
Using a privacy-focused tool limits exposure at the collection phase. The Swetrix Data Policy describes a standard analytics model that uses no cookies or client-side identifiers. The platform says it processes incoming IP information temporarily to derive a session identifier without storing the raw IP address. This approach can reduce analytics-related tracking friction while supporting campaign attribution, referral reporting, and custom event tracking.
For teams comparing a Google Analytics replacement, those collection practices can be considered alongside the product data needed to understand user journeys. Swetrix also offers conversion funnels and A/B testing, so a cookieless analytics approach can support growth measurement without requiring teams to abandon those product analytics workflows. Technical SEO insights and other specialist reporting should remain on your evaluation checklist, with each capability verified against the tools you plan to use.
Review Roles, Requests, and Vendor Contracts
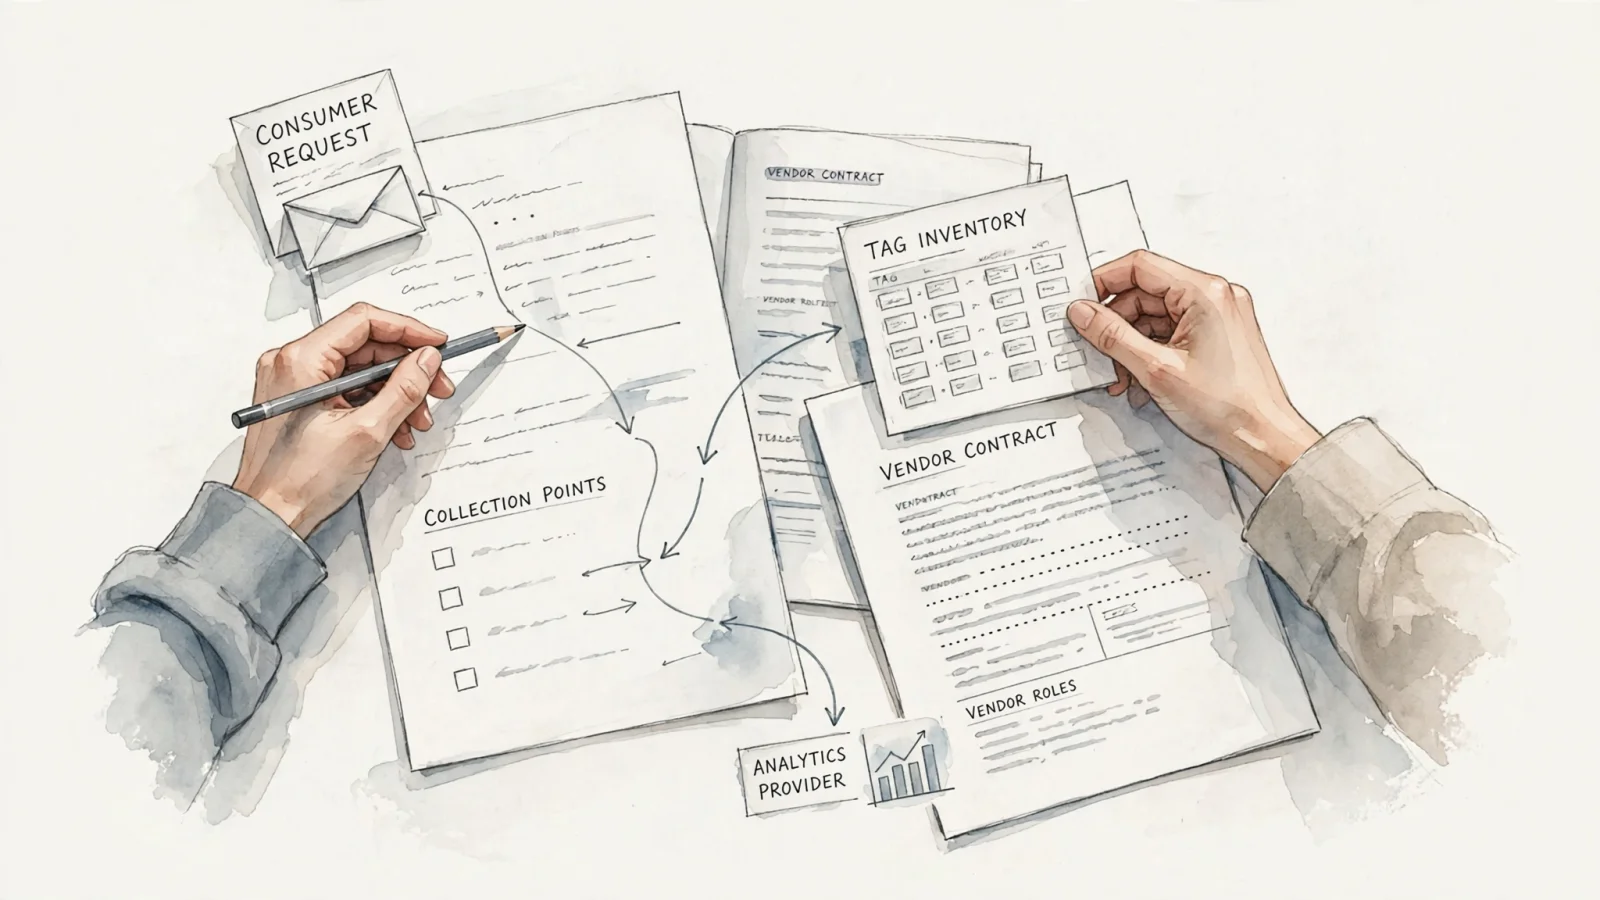
Once you understand what data leaves the browser, map out each party's role in processing it by reading your vendor contracts to determine permitted data uses, deletion responsibilities, and applicable California opt-outs. A vendor's status as a service provider or data processor depends on actual data flows and contractual limits, not its marketing material.
B2B analytics providers handling end-user requests should map how deletion requests flow through the product architecture. If a California resident requests deletion, the CPPA says the resident can ask the business to delete personal information collected from them and to tell its service providers to do the same, subject to exceptions such as legally required retention, as the CPPA's deletion-rights FAQ explains. So analytics providers should design data flows that make relevant records easy to locate and delete.
Treat Session Replay as a Separate Review
Standard traffic measurement and session replay need separate privacy reviews because replay features can capture page state, user interactions, mouse movements, and some non-password input values. Recording starts only when a site executes a specific function, such as startSessionReplay().
Deploying session replays raises the risk of capturing sensitive personal data. Swetrix mitigates this through a default total privacy mode that automatically masks text and inputs before they leave the browser. Despite these protections, you must review masking configurations, privacy notices, and selected legal bases before activating recordings. On pages containing medical information, financial forms, or private account details, session replay may require prior consent or another valid legal condition depending on the data captured and the rules that apply, because cookieless tracking alone does not settle the privacy requirements for these recordings.
The Verdict: Which Rules Apply to Your Website?
Jurisdictional reach determines your obligations. If your processing meets the GDPR's territorial test because your organization is established in the EU, offers goods or services to people there, or monitors their behavior there, you must establish a lawful basis for every processing purpose and evaluate device-access rules separately. If your business falls within the CCPA's coverage test, you must operationalize transparent notices, consumer rights protocols, sale and sharing opt-outs, and strict vendor contract terms.
Both laws can apply to the same website simultaneously. For example, a Berlin software company that offers services to people in the EU and does business in California may need to comply with both frameworks if it also meets a CCPA threshold, addressing GDPR obligations for its EU users and honoring California opt-outs when its practices qualify as a sale or share.
If you want to reduce the regulatory burden of your web traffic measurement, Swetrix is a strong Google Analytics alternative. By using a cookieless model that temporarily processes IP information to derive session identifiers, the platform offers metrics like conversion funnels and A/B testing. This can reduce some device-storage-related compliance work, but teams still need to assess their data flows and identify an appropriate lawful basis. You can explore how cookieless tracking works to review how the approach fits your marketing efforts.
Common Questions
Does cookieless analytics always bypass consent requirements? Cookieless analytics can avoid ePrivacy consent rules for device storage and access when the tool does not store or read information on a visitor's device, but personal-data processing still needs an appropriate GDPR lawful basis. A tool that fingerprints browsers to build identifiable profiles may still implicate device-access rules and data-protection requirements under national law.
Does the CCPA require a cookie banner? The CCPA focuses on notice at collection and opt-out rights rather than requiring prior opt-in consent for every tracker. Covered businesses must honor applicable opt-out preference signals and provide an appropriate opt-out method when analytics use qualifies as a sale or sharing.
Can CCPA and GDPR apply at the same time? A website may be subject to both frameworks if its processing falls within the GDPR's territorial scope and the operator meets a CCPA coverage test for information collected from California residents. Site owners can use separate controls for each jurisdiction or adopt a broader baseline, but they need to meet the specific requirements that apply in each.
Does the CCPA cover B2B contacts? The CPPA says CCPA rights extend to California residents who are employees, job applicants, and contacts for business customers, vendors, or independent contractors. B2B software companies that collect personal information about California-resident contacts should account for that data if their business meets the CCPA coverage test.
Are the CCPA and CPRA separate laws? The California Privacy Rights Act amended the existing California Consumer Privacy Act, meaning they operate as a single consolidated legal framework governing privacy rights for California residents.
Stop wrestling with complex consent configurations and start understanding your visitors. Swetrix provides a fully open-source, cookieless analytics platform designed to protect user privacy without sacrificing the product and marketing data you need to grow. For teams moving away from Google Analytics, Swetrix bridges straightforward privacy-focused tracking with advanced product analytics, including conversion funnels and A/B testing, while its session replay capabilities can help you examine user journeys under appropriate privacy safeguards. Transition away from intrusive tracking today at Swetrix.com.